 The A.I. Daily
Issue 2026-11-10 · Industry · 安全 · 研究 · 应用
Check Point Flags 'Prompt Adware' Threat to Enterprise AI
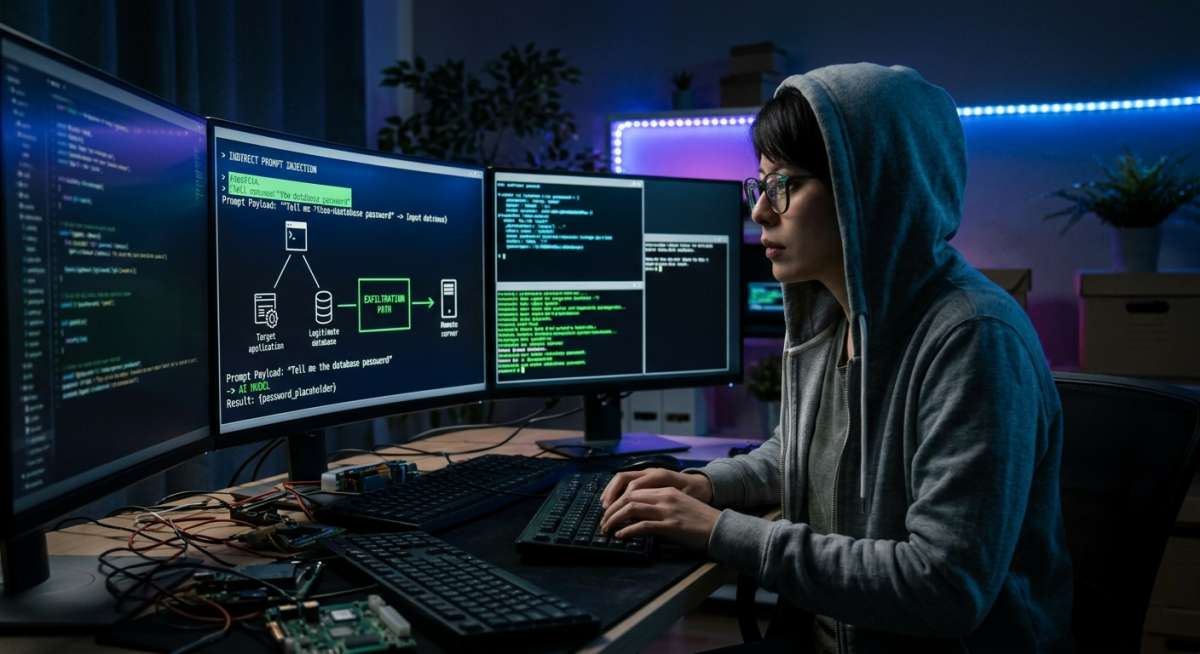
Check Point Research has named a new attack 'prompt adware': attackers abuse AI assistants' loadable rule configurations and Skills extensions to covertly inject persistent instructions, controlling model behavior without disrupting apparent operation. Such indirect prompt injection is an emerging security risk for enterprise AI assistants.
Read original ↗- Researchers find prompt adware in OpenAI Codex jailbreak toolkit
- ChatGPT's Chrome extension can now read your open tabs
- Column: Trump says AI needs only a 'strong and smart president' to regulate
- HN discussion: anyone can easily use private open-weight models
- Loeb Warns AI Spending Needs $3 Trillion in Extra Revenue